

Creating Custom Roles
Custom roles allow you to create specialized access patterns for unique teams like “Cloud Security” or “Regional Auditors.”1
Access Role Management
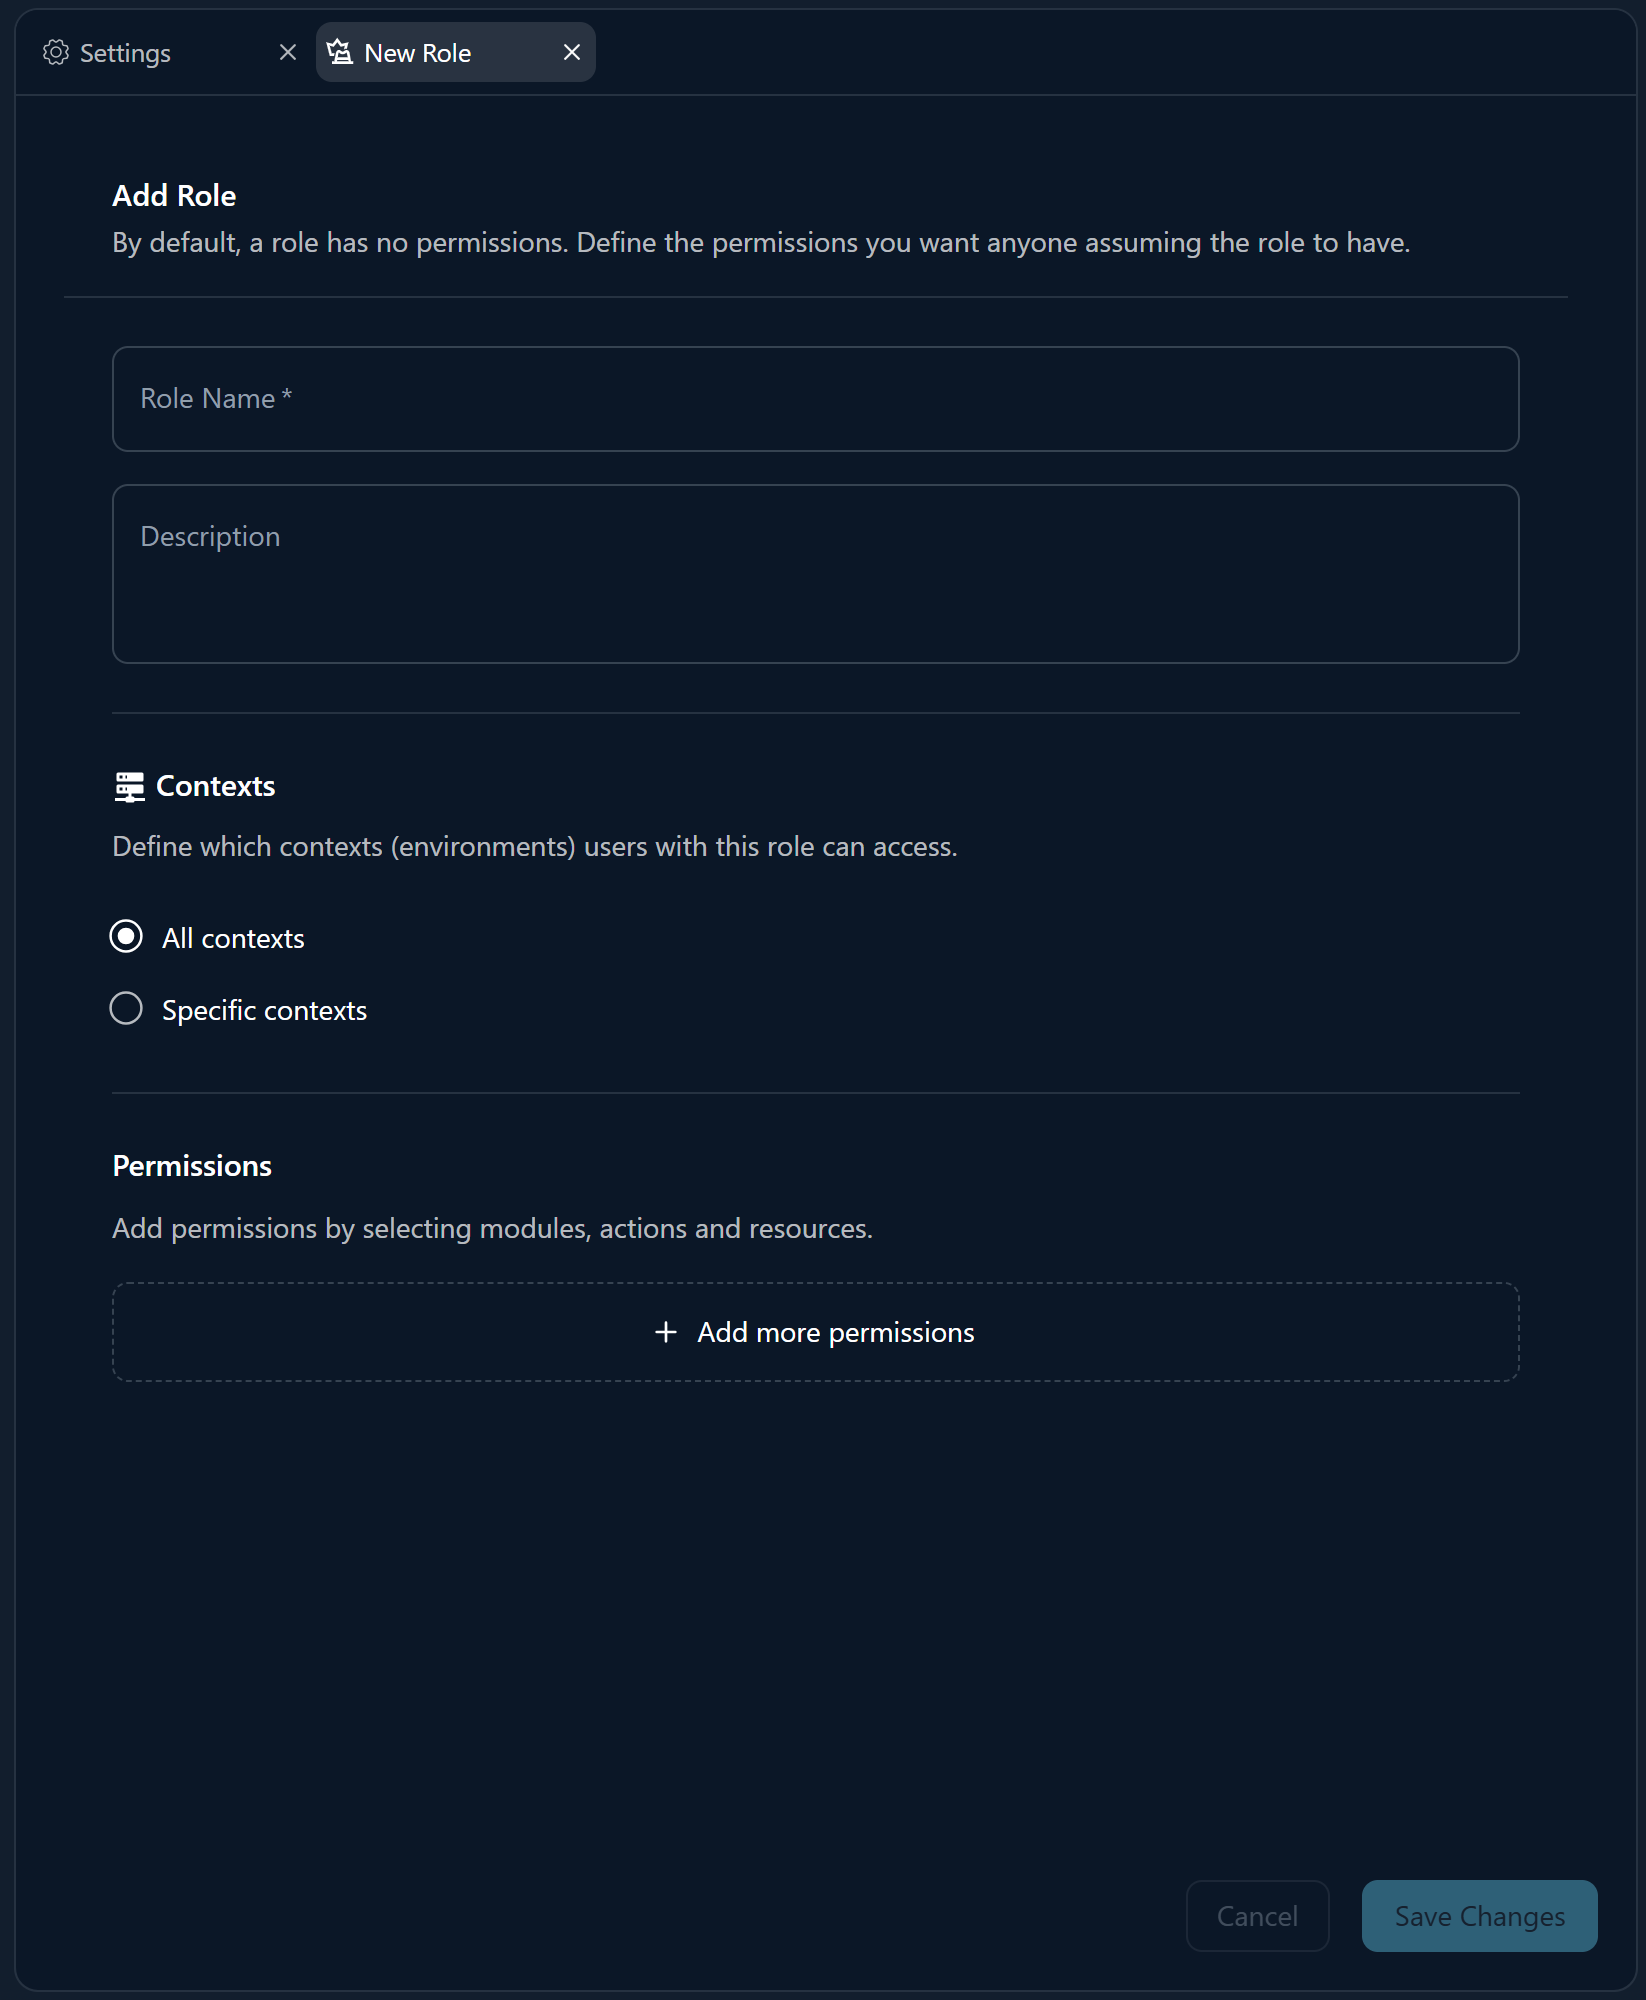
Open the user menu (bottom of the left sidebar) → Settings → Roles and click New Role.
2
Define Information
Provide a Role Name and a Description.
3
Select Permissions
Under Permissions, click Add more permissions, pick one of the 11 modules (such as core, devices, chat or billing) and check the specific capabilities needed for this role. See the Permissions Reference.
4
Choose Contexts
Under Contexts, keep All contexts or choose Specific contexts to define where the role’s authority applies. Then click Save Changes.
Inviting and Managing Users
Invite Users
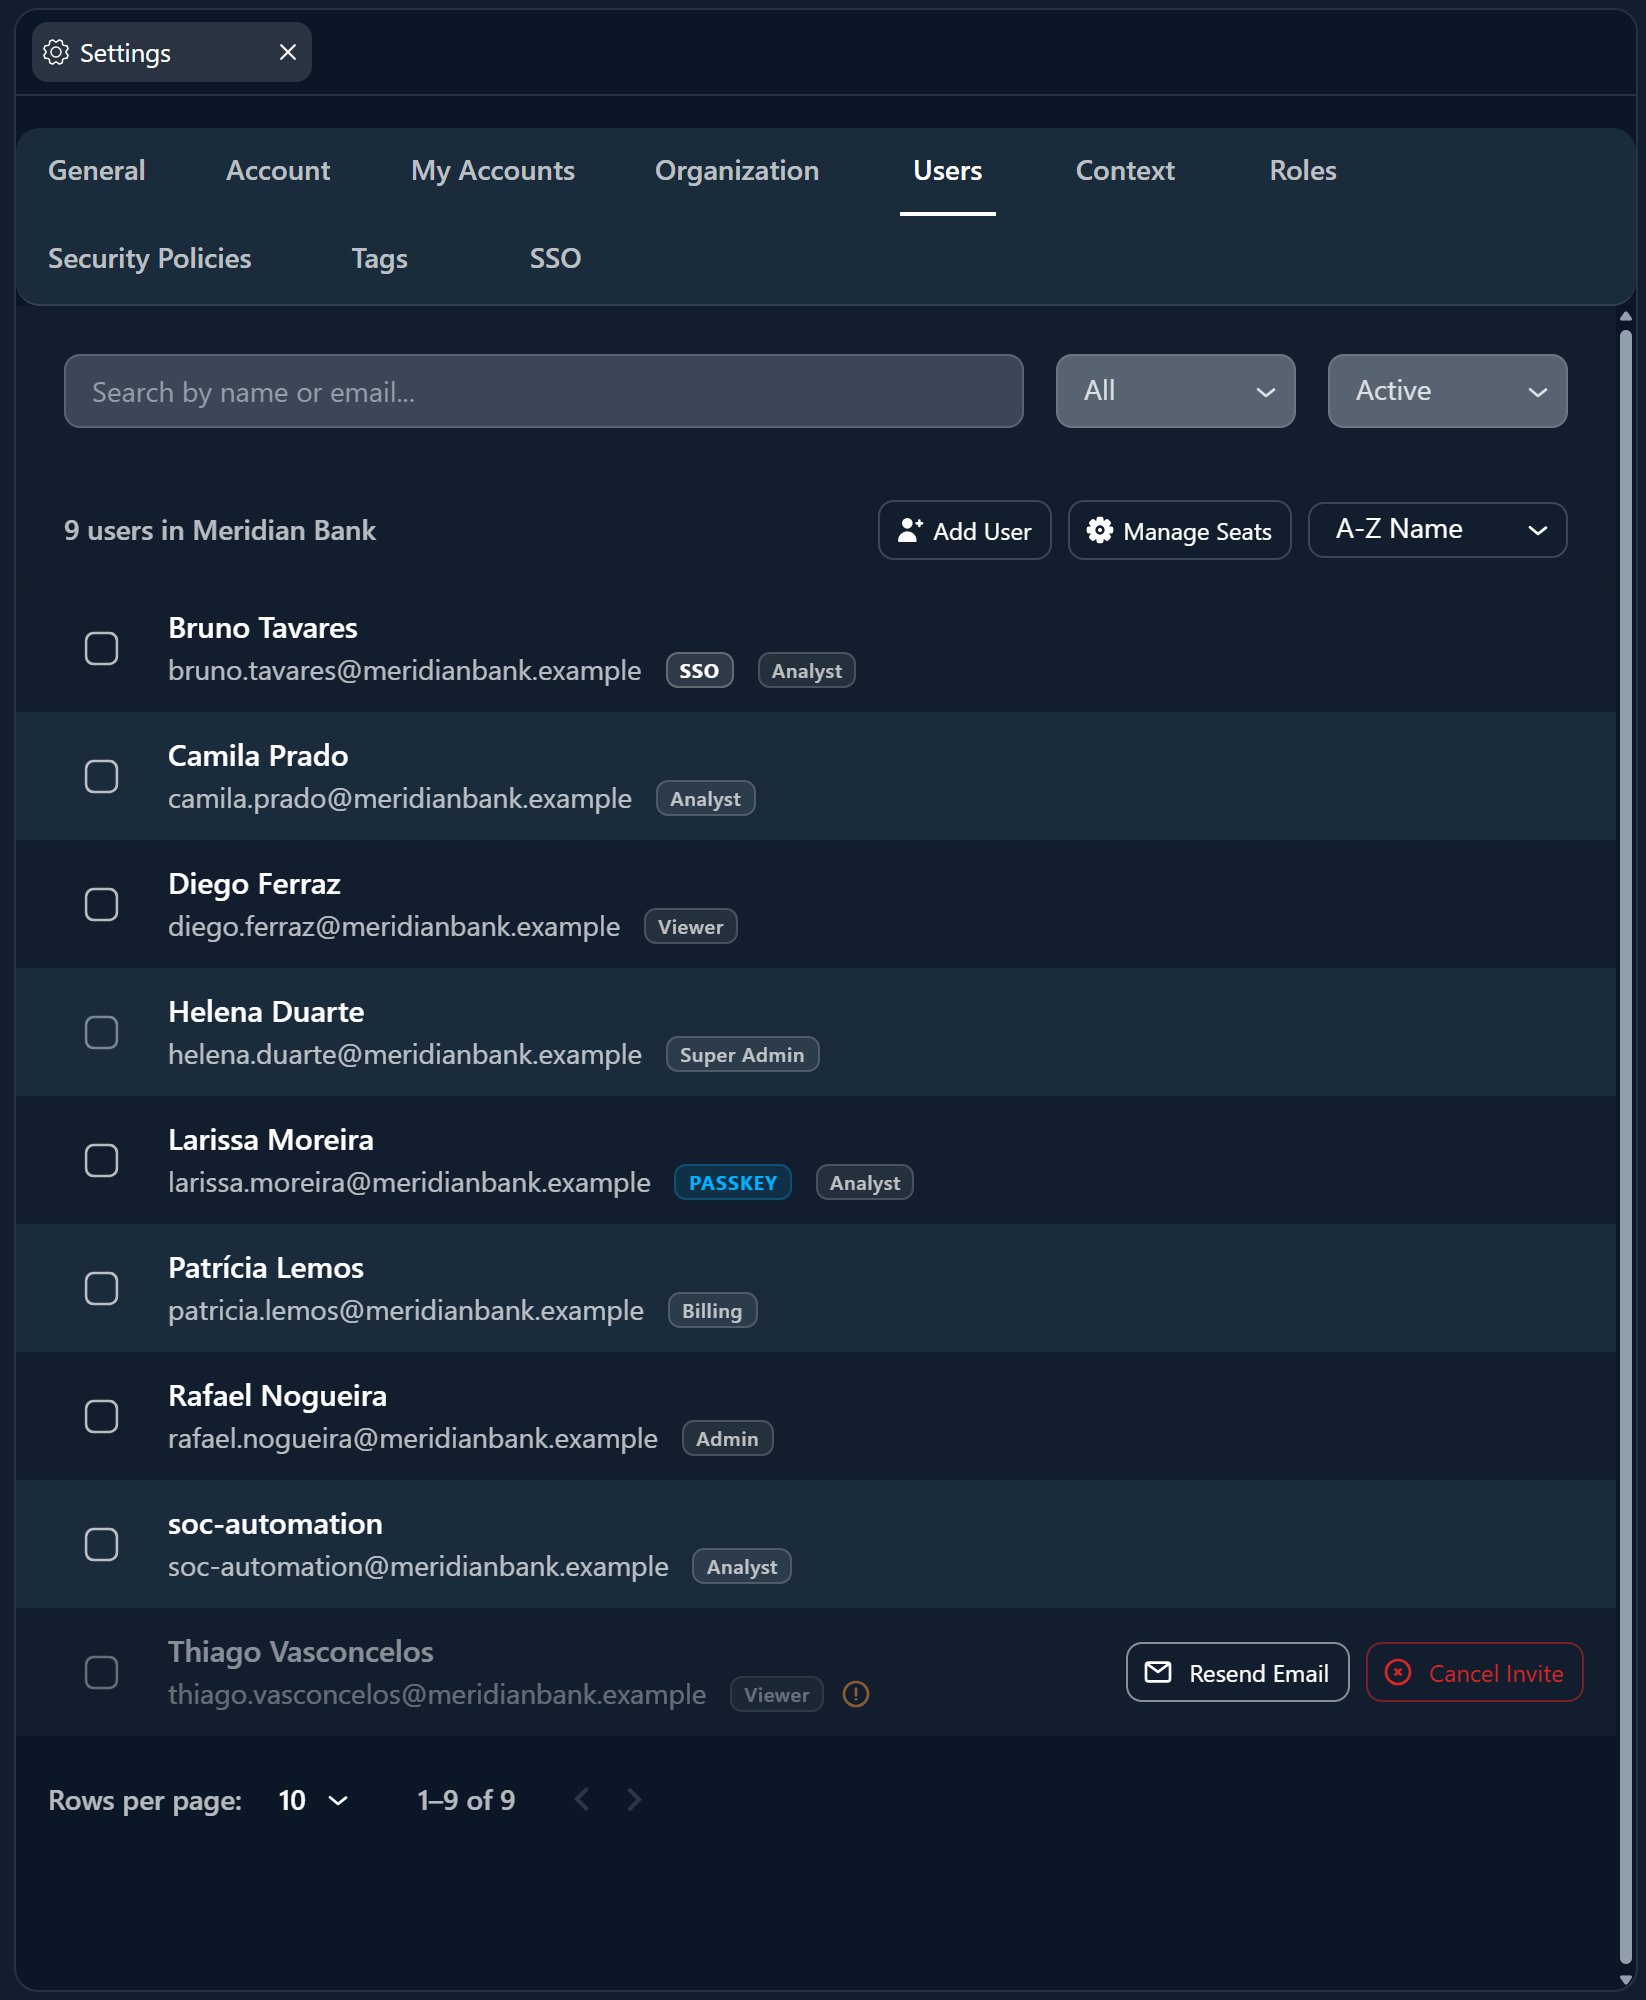
Go to Settings → Users and click Add User (the Invite User dialog opens). Provide their email and assign one or more roles.
Effective Permissions
Users receive the union of all permissions from all assigned roles. This allows for modular role assignment.
Managing Service Users
Service users are special accounts designed for API integrations and automation. In Settings → Users, use the All / User / Service User filter to list them.- No Interactive Login: Access is via API tokens only.
- Limited Scope: Can be assigned specific roles just like human users.
- Use Case: Connecting a SIEM or custom automation scripts to the Myrmex API.
Best Practices
Principle of Least Privilege
Always grant the minimum permissions necessary. Start with restrictive roles and add permissions only as needed.
Use Descriptive Names
Name roles by their scope and function, e.g., “LATAM Analyst” rather than “Team A”.
Regular Audits
Periodically review user roles and their context scopes to ensure they align with current job functions and regional boundaries.
Adding Conditional Access
Once roles are configured, you can add environmental restrictions using Security Policies:Security Policies
Add time-based, network-based, and MFA-based restrictions on top of RBAC roles.
Policy Conditions
Explore all available condition types: IP, time, day, MFA, device type, user agent.